OPNsense
You set up a VLAN in OPNsense in three moves: create the VLAN device with a parent interface and a tag (for example device vlan0.20 on your LAN port with tag 20), assign that device as an interface while the parent stays unassigned, then give the new interface its own subnet, DHCP and firewall rules. The matching switch port must carry the same tag, and a device plugged into a port set for that VLAN should land in the new subnet and be governed by your rules. Everything below follows that flow, in that order.
What a VLAN actually buys you
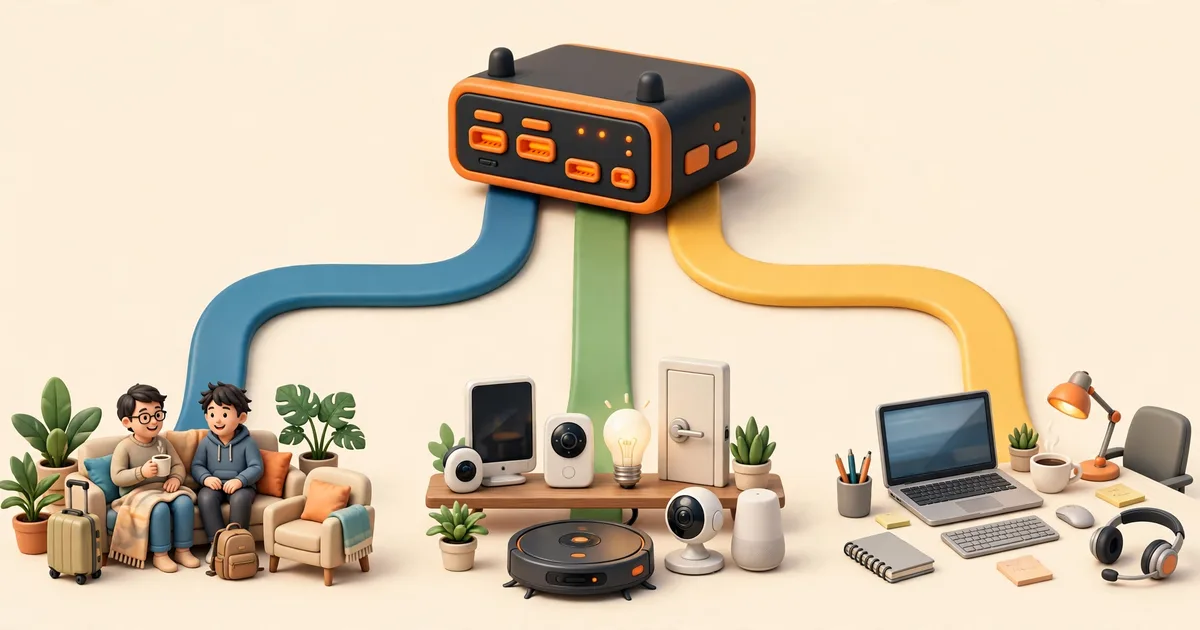
A virtual LAN lets one physical network carry several separate logical networks. The separation is done with a small tag added to each frame, a number between 1 and 4094 that says which network the frame belongs to. OPNsense routes and firewalls between these networks exactly as it does between physical interfaces, so a VLAN is how you get a guest network, an IoT network, or a work network without buying a second firewall or running a second set of cables. Typical home uses look like this:
| VLAN | Example tag | Example subnet | Typical policy |
|---|---|---|---|
| Main LAN | untagged or 1 | 192.168.1.0/24 | Trusted, reaches most things |
| Guest | 20 | 192.168.20.0/24 | Internet only, no LAN access |
| IoT | 30 | 192.168.30.0/24 | Internet plus a few named LAN hosts |
| Work | 40 | 192.168.40.0/24 | Isolated, like guest, with its own rules |
The official guidance suggests embedding the tag in the subnet (tag 20 living on 192.168.20.0/24, and so on). It is only a convention, but months later, when an address appears in a log, you will be glad the mapping is obvious.
What you need before starting
- A free physical interface on OPNsense to act as the parent (often the LAN port itself), or a LAGG if you bond ports to the switch.
- A managed switch that understands 802.1Q VLAN tags. Unmanaged switches cannot assign tags to ports, and without that, end devices cannot join a VLAN. This is the requirement that stops most first attempts, so check the switch before you configure anything.
- A plan on paper: tag numbers, subnets, and which switch ports belong to which VLAN.
- A configuration backup (System > Configuration > Backups). VLAN work involves interface assignment, and a backup turns a mistake into a restore instead of a rebuild. See our backup and restore guide for the exact clicks.
Step 1: Create the VLAN device
In the GUI, go to the VLAN device settings (Interfaces > Other Types > VLAN) and add a device. Three settings define it:
- Parent interface: the physical interface the tagged traffic rides on, for example your LAN NIC. The parent carries the frames; the VLAN device is the logical network on top of it.
- VLAN tag: the number for this network, for example 20.
- Device name: OPNsense proposes a name in the pattern of vlan0.20, combining the device and the tag. Accept the pattern; consistent names make logs and rules readable.
Save the device. At this point it exists but does nothing: a VLAN device that is not assigned as an interface has no address, no DHCP, and no rules.
Step 2: Assign the VLAN as an interface
Go to Interfaces > Assignments and add the new VLAN device as an interface, giving it a recognisable description such as GUEST. Two rules of the road here:
- The parent interface stays unassigned when it serves purely as the VLAN carrier. The official how-to is explicit about this: the parent is the trunk, the VLAN devices are the networks.
- Enable the new interface and set its IPv4 configuration to Static, with the first address of its subnet, for example 192.168.20.1/24 for tag 20. Each VLAN interface needs its own unique network; two interfaces cannot share a subnet.
If you skipped VLANs during the initial console setup, that is fine and normal: the installer offers them, but the official install guidance expects most people to answer no there and do exactly this GUI flow later.
Step 3: Configure the switch trunk and access ports
OPNsense is now sending and expecting tagged frames on the parent port, and the switch must agree. On the switch:
- Set the port that connects to OPNsense as a trunk (tagged) port carrying your VLAN tags, including 20.
- Set the ports where end devices plug in as access (untagged) ports for their VLAN: a port set to VLAN 20 puts whatever plugs into it onto the guest network, and the device itself never sees a tag.
- For Wi-Fi, map each SSID to a VLAN on the access point, so the guest SSID lands guests on VLAN 20 while your main SSID stays on the LAN.
One best practice from the official documentation is worth following exactly: do not mix tagged and untagged traffic on the trunk between OPNsense and the switch. Keep the native or default VLAN off that trunk port. Mixed setups can work on paper and then leak traffic between networks in ways that defeat the point of segmenting at all. If you connect OPNsense to the same switch with several cables, the same guidance says to use a LAGG (LACP) rather than a bridge, to avoid loops.
Step 4: DHCP and DNS for the new network
A VLAN interface without DHCP leaves every guest device to configure itself, which in practice means no connection. Enable the DHCP service for the new interface with a sensible range inside its subnet (for example 192.168.20.100 to 192.168.20.200 on the guest network), leaving the low addresses free for the gateway and any static assignments. Devices on the VLAN will then receive an address, the gateway (the VLAN interface address), and DNS. If you changed your main LAN addressing recently, the pattern matches the one in our guide to changing the OPNsense LAN IP: address, range, and gateway must always agree.
Step 5: Firewall rules, the actual point of the exercise
A new interface in OPNsense starts with no pass rules, which means its devices can reach nothing, not even the internet. That blank slate is a feature: you add exactly the access this network should have. For a guest VLAN, a typical minimal set is:
- Allow the guest network to reach the internet (destination: anything that is not your private networks).
- Block the guest network from the LAN and your other VLANs explicitly, or rely on the inverse allow above to do it. Many admins write both: a block rule to private ranges first for clarity in the logs, then the allow.
- Allow DNS to the firewall itself if your rule set would otherwise block it, so guests can resolve names.
For an IoT VLAN the pattern differs slightly: allow the internet, allow replies to controllers on the LAN by permitting specific LAN hosts to open connections into the IoT network (rules on the LAN interface), and leave the IoT network itself unable to start conversations with the LAN. Cross VLAN traffic is ordinary routed traffic to OPNsense, so every one of these decisions is just a firewall rule on the source interface. If you also run Suricata IDS/IPS, decide per interface whether the new VLAN is inspected, the same as any other interface.
Confirm it worked
- Plug a laptop into a switch port assigned to the VLAN (or join the guest SSID). It should receive an address in the VLAN subnet, with the VLAN interface as its gateway.
- From that device, open a public website: the internet should work if your rules allow it.
- From the same device, try to open the firewall's LAN address or a LAN server: it should fail for guest and IoT networks. This negative test is the one that proves segmentation is real.
- Check the DHCP leases view on OPNsense: the device should appear under the VLAN interface, confirming it landed where you intended.
- Finally, check a device on the main LAN still works exactly as before. VLAN changes should be invisible to networks you did not touch.
Troubleshooting by symptom
Devices on the VLAN get no IP address
Work along the path: is the VLAN device created with the right parent and tag; is it assigned and enabled with a static address; is DHCP enabled on that interface with a valid range; and is the switch port actually set to this VLAN? The switch is the most common culprit, followed by DHCP simply not being enabled on the new interface.
Devices get an address in the wrong subnet
The port or SSID is mapped to a different VLAN than you think, or the trunk is carrying an untagged network that devices fall into. Recheck the access port's VLAN assignment and keep untagged traffic off the trunk, as the official guidance recommends.
The VLAN reaches the internet but also reaches the LAN
Your allow rule is too broad: it passes everything, including private ranges. Narrow it so the allowed destination excludes your local networks, or add an explicit block to the LAN network above the allow rule. Then rerun the negative test until the LAN address stops answering.
Nothing on the VLAN works at all, including the gateway
If a device has a correct address but cannot even reach the VLAN interface address, suspect the tag path: parent interface mismatch, a trunk port missing this tag, or the parent interface accidentally assigned and enabled with its own configuration fighting the VLANs. Remember the rule: parent unassigned, VLANs assigned.
One specific device refuses to join
Some cheap IoT devices and older printers handle tagged environments and new DHCP offers poorly. Test the same port with a laptop first; if the laptop works, the network is fine and the device is the problem, and a static lease or a different port setting usually settles it.
Intermittent: some VLAN devices drop off and return
Flapping usually lives in the physical layer of the trunk: a marginal cable between firewall and switch, a switch port negotiating oddly, or power saving features on a NIC putting the link to sleep. Swap the trunk cable first, then check both ends of the link for errors, and only then revisit the configuration. Configuration mistakes are steady and reproducible; hardware faults come and go with temperature and vibration, and the pattern of the failures tells you which one you have.
Growing the setup
Once one VLAN works end to end, adding the next is a repeat of the same five steps with a new tag and subnet, which is why the written plan matters. Networks worth adding after guest are usually IoT and a separate work network. Remote access fits naturally on top of segmentation too: a WireGuard tunnel can land its peers in their own network with rules that reach only what you choose, instead of dropping remote devices straight onto your trusted LAN.
Planning tags like you will own them for years
Because you will. VLAN tags are easy to create and annoying to renumber once switches, access points, and a dozen rules all reference them, so spend ten minutes on the scheme before the first device exists. Leave gaps between numbers (10, 20, 30 rather than 1, 2, 3) so a future network can slot between existing ones. Keep a small written register: tag, subnet, purpose, which switch ports and SSIDs carry it. When you add a second switch later, that register is the difference between an hour of configuration and a weekend of archaeology.
One more planning decision: whether the main LAN itself stays untagged or moves onto a tag as well. Many home setups leave the trusted LAN untagged for simplicity and tag only the additional networks, which is perfectly workable as long as the trunk rule from Step 3 is respected for the tagged side. Others tag everything for symmetry. Either is defensible; mixing approaches halfway, with some switches expecting the LAN untagged and others tagged, is where the confusing failures live. Pick one, write it in the register, and be consistent across every switch and access point you own.
Segmentation is the highest value change most home networks ever get: one afternoon of tags and rules, and a compromised gadget stops being a skeleton key to everything you own.